利用修改邻接变量

资源下载
【免费】突破密码认证程序(修改邻接变量)资源-CSDN文库
资源内容
源码
/*****************************************************************************To be the apostrophe which changed "Impossible" into "I'm possible"!
POC code of chapter 2.2 in book "Vulnerability Exploit and Analysis Technique"
file name : stack_overflow_var.c
author           : failwest
date       : 2006.9.20
description    : demo show nearby var overrun in stackinput 8 letters to bypass authentication
Noticed         : complied with VC6.0 and build into begug version
version          : 1.0
E-mail           : failwest@gmail.com            Only for educational purposes    enjoy the fun from exploiting :)
******************************************************************************/
#include <stdio.h>
#define PASSWORD "1234567"
int verify_password (char *password)
{int authenticated;char buffer[8];// add local buffauthenticated=strcmp(password,PASSWORD);strcpy(buffer,password);//over flowed here!    return authenticated;
}
main()
{int valid_flag=0;char password[1024];while(1){printf("please input password:       ");             scanf("%s",password);            valid_flag = verify_password(password);            if(valid_flag){printf("incorrect password!\n\n");}else{printf("Congratulation! You have passed the verification!\n");break;}}
}
其实是对上一个文章的源码修改
请注意一下的两个修改
(1)verify_passowrd()函数的局部变量buffer[8]
(2)字符比较后strcpy(buffer,password)这个函数时c语言的高危函数,很容易出现栈溢出
流程
密码还是1234567
这里直接用动态调试就可以
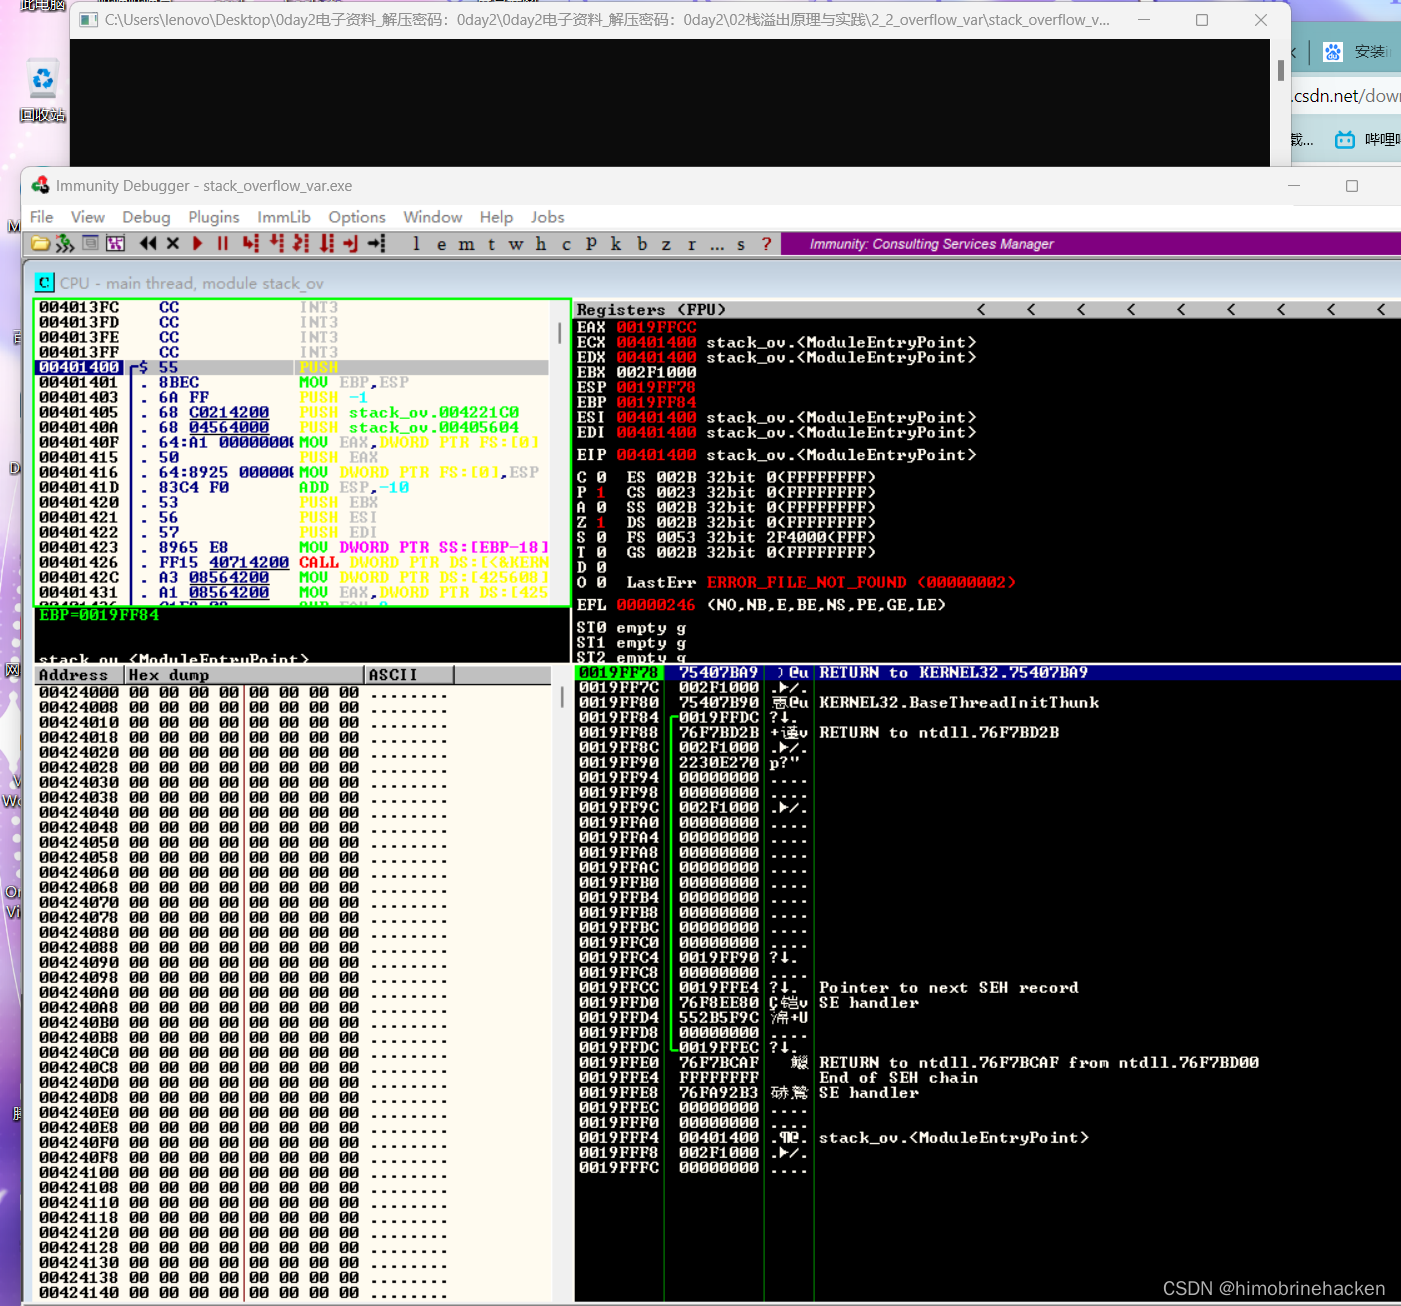
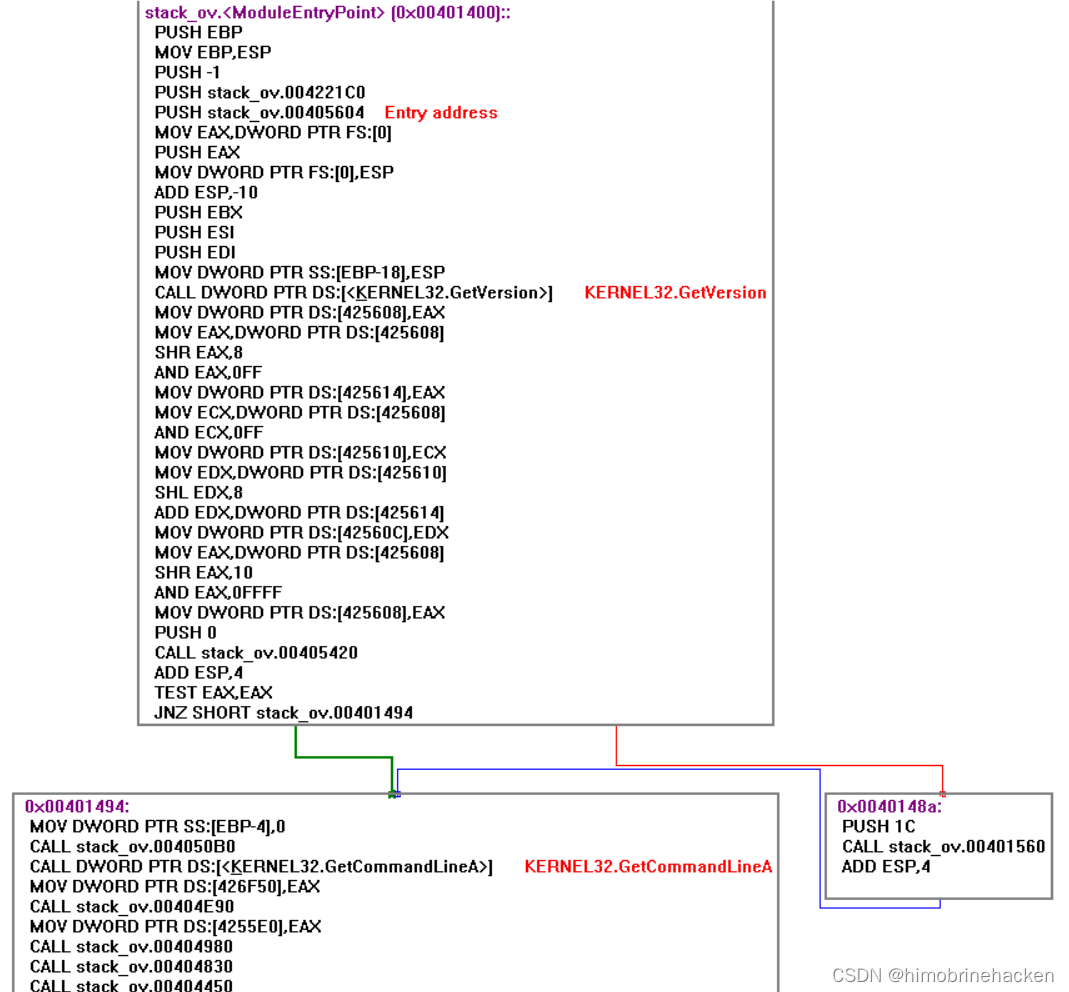
这里是呢我那个看到分支的

直接运行一下
当我们输入的密码不正确的时候strcmp应该返回1(authenticated是1)
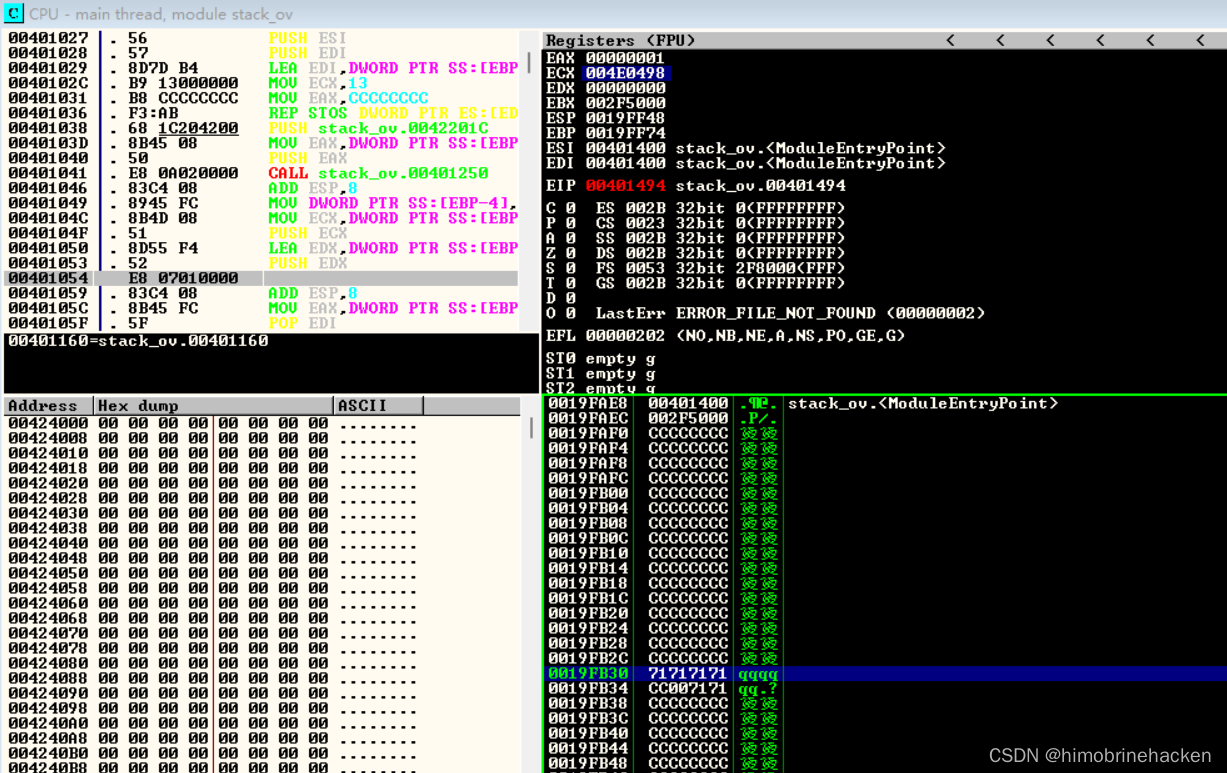


| 局部变量名 | 内存地址 | 偏移3的值 | 偏移2的值 | 偏移1的值 | 偏移0的值 |
| buffer[0-3] | 0x0019FB30 | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) |
| buffer[4-7] | 0x0019fb34 | NULL | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) |
| authenticated | 0x0019FF30 | 0x00 | 0x00 0x00 0x01 |
接下来我们需要输入超过这个字符的字符试试能不能写进authenticated
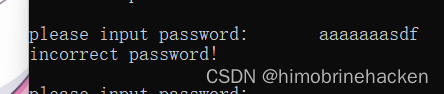
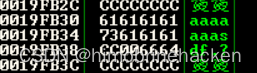

| 局部变量名 | 内存地址 | 偏移3的值 | 偏移2的值 | 偏移1的值 | 偏移0的值 |
| buffer | 0x0019FB30 | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) |
| 0x0019fb34 | NULL | 0x71(’q’) | 0x71(’q’) | 0x71(’q’) | |
| authenticated覆盖前 | 0x0019FF30 | 0x00 | 0x00 0x00 0x01 | ||
| authenticated覆盖后 | 0x0019FF30 | 0x00 | 0x00 | 0x66(‘f’) | 0x64(‘d’) |
已知溢出之后能修改authenticated,那我们只需将数据溢出到buffer的边界那么这段溢出数据刚好就可以将authenticated修改成0
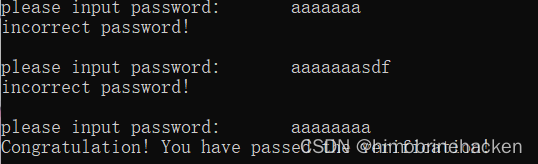
但是

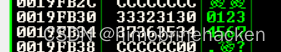
此时是-1